

Activity Logs are available only to organization owners.
Accessing Activity Logs
On the Organizations page, select Activity Logs in the sidebar.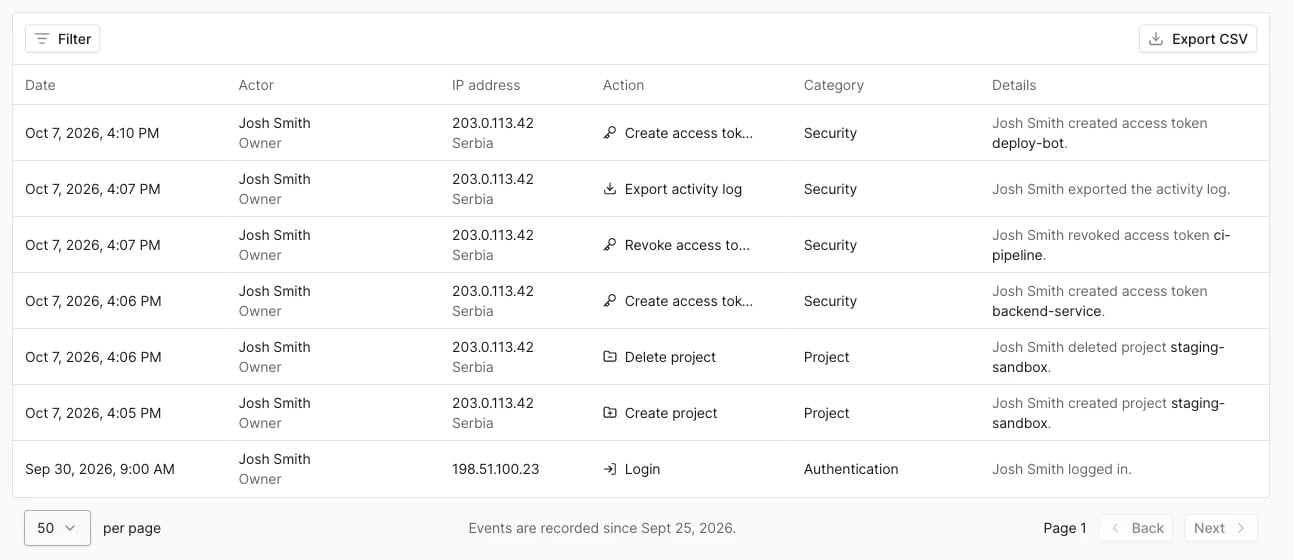
Reading the table
Each row shows:
Hover over an Actor, Action, or Category cell and click its filter icon to filter the log by that value.
Event details
Click a row to open the details panel.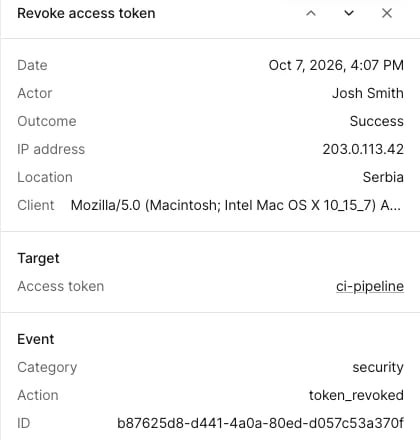
- Summary: date, actor, outcome, the error code and message for failed events, IP address, location, and client (the request’s
User-Agentheader). - Target: the resource the action was performed on, such as an access token, member, or project, and the project the event belongs to.
- Changes: before and after values. Recorded for member permission changes and project transfers.
- Event: the raw category and action keys (for example
securityandtoken_revoked) and the event ID, which match the corresponding columns in the CSV export.
Filtering and pagination
Filter by date and time, actor, action, category, project, actor type (user, access token, or unauthenticated), and status (success, failed, or denied). Filter values are populated from your organization’s actual history, so departed members and revoked tokens remain filterable. Activity Logs started recording on September 25, 2026. Events from before that date aren’t available. The date filter and the table footer both note this start date. Your filters and the selected event are reflected in the URL, so a view can be bookmarked or shared and survives a page reload. Choose 10, 20, 50, or 100 rows per page.Exporting logs
Click Export CSV to download the currently filtered log asactivity-logs-<organization>-<date>.csv. If the filtered log has more rows than a direct download allows, the dashboard offers a background export instead: after you confirm, a time-limited download link is emailed to your account email once the file is ready. Each export is recorded in the log as an Export activity log event.
The CSV has one row per event, newest first, with these columns:
Tracked actions
Activity Logs record these actions:
Authentication events belong to the user rather than to one organization, so they appear in the Activity Logs of every organization the user is a member of.
Activity Logs cover access, account custody, and billing: who can act, what credentials and secrets exist, whether the organization and its projects exist, and changes to payment methods and subscriptions. Changes to the contents of a project, such as alerts, Virtual Environments, nodes, contracts, and wallets, aren’t included.